Missing Authorization for Interactive Sessions
June 9, 2025
Products Impacted
This vulnerability is present in all versions of BackendAI. We tested on version 25.3.3 (commit f7f8fe33ea0230090f1d0e5a936ef8edd8cf9959).
CVSS Score: 8.1
CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H
CWE Categorization
CWE-862: Missing authorization
Details
When a user starts an interactive session, a web terminal gets exposed to a random port. A threat actor can scan the ports until they find an open interactive session and access it without any authorization or prior authentication.
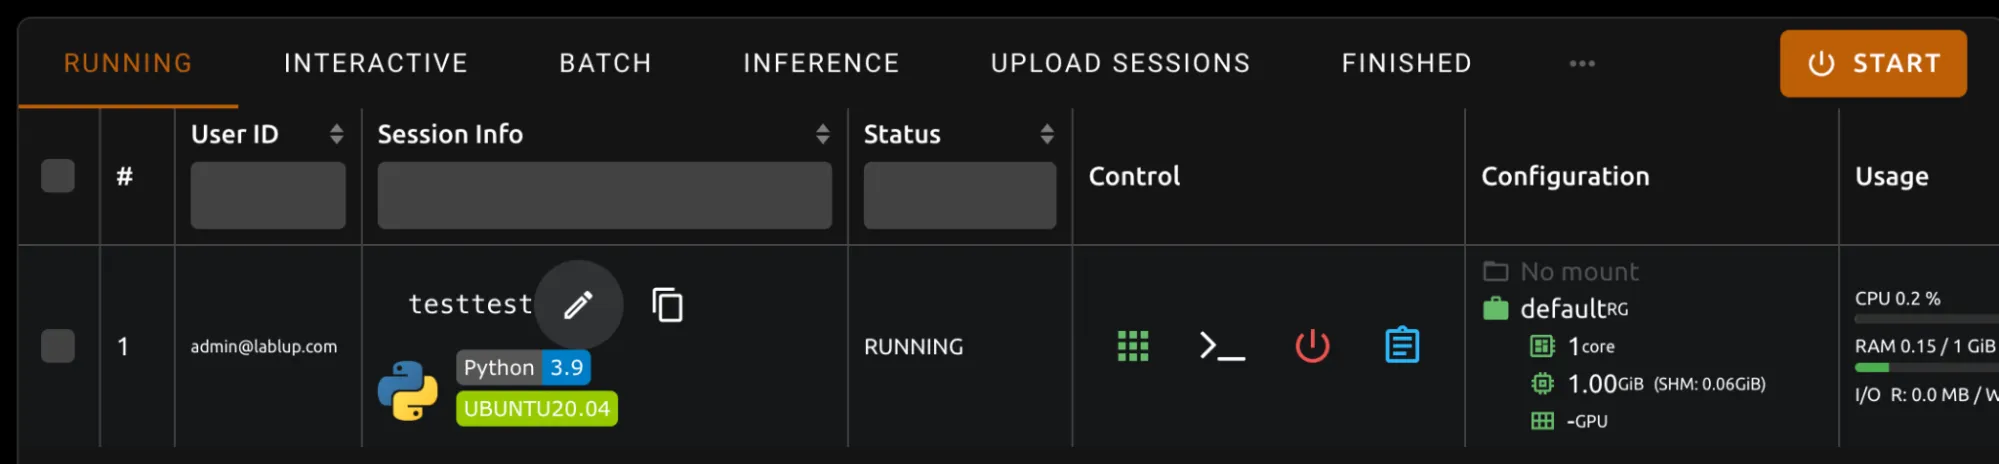
To reproduce this, we created a session with all settings set to default.
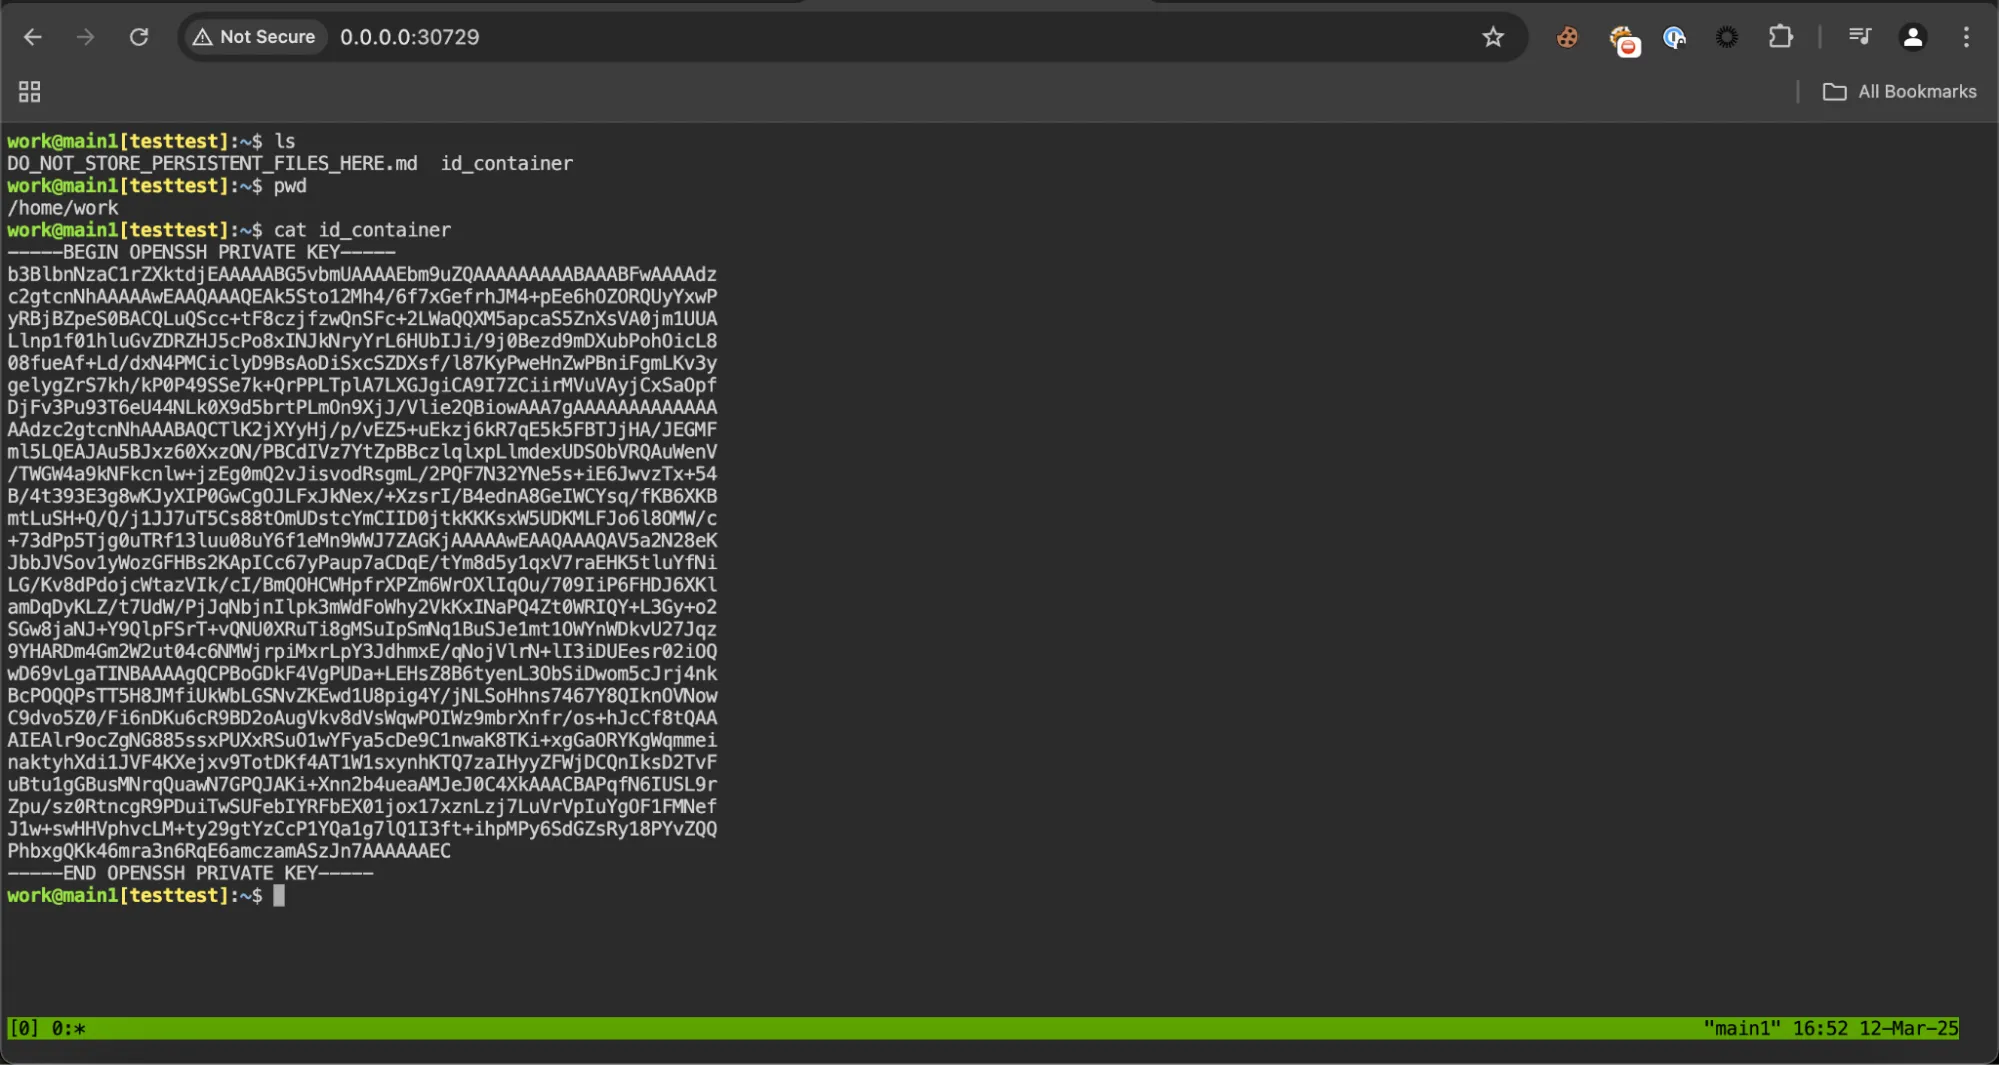
Then, we accessed the web terminal in a new tab
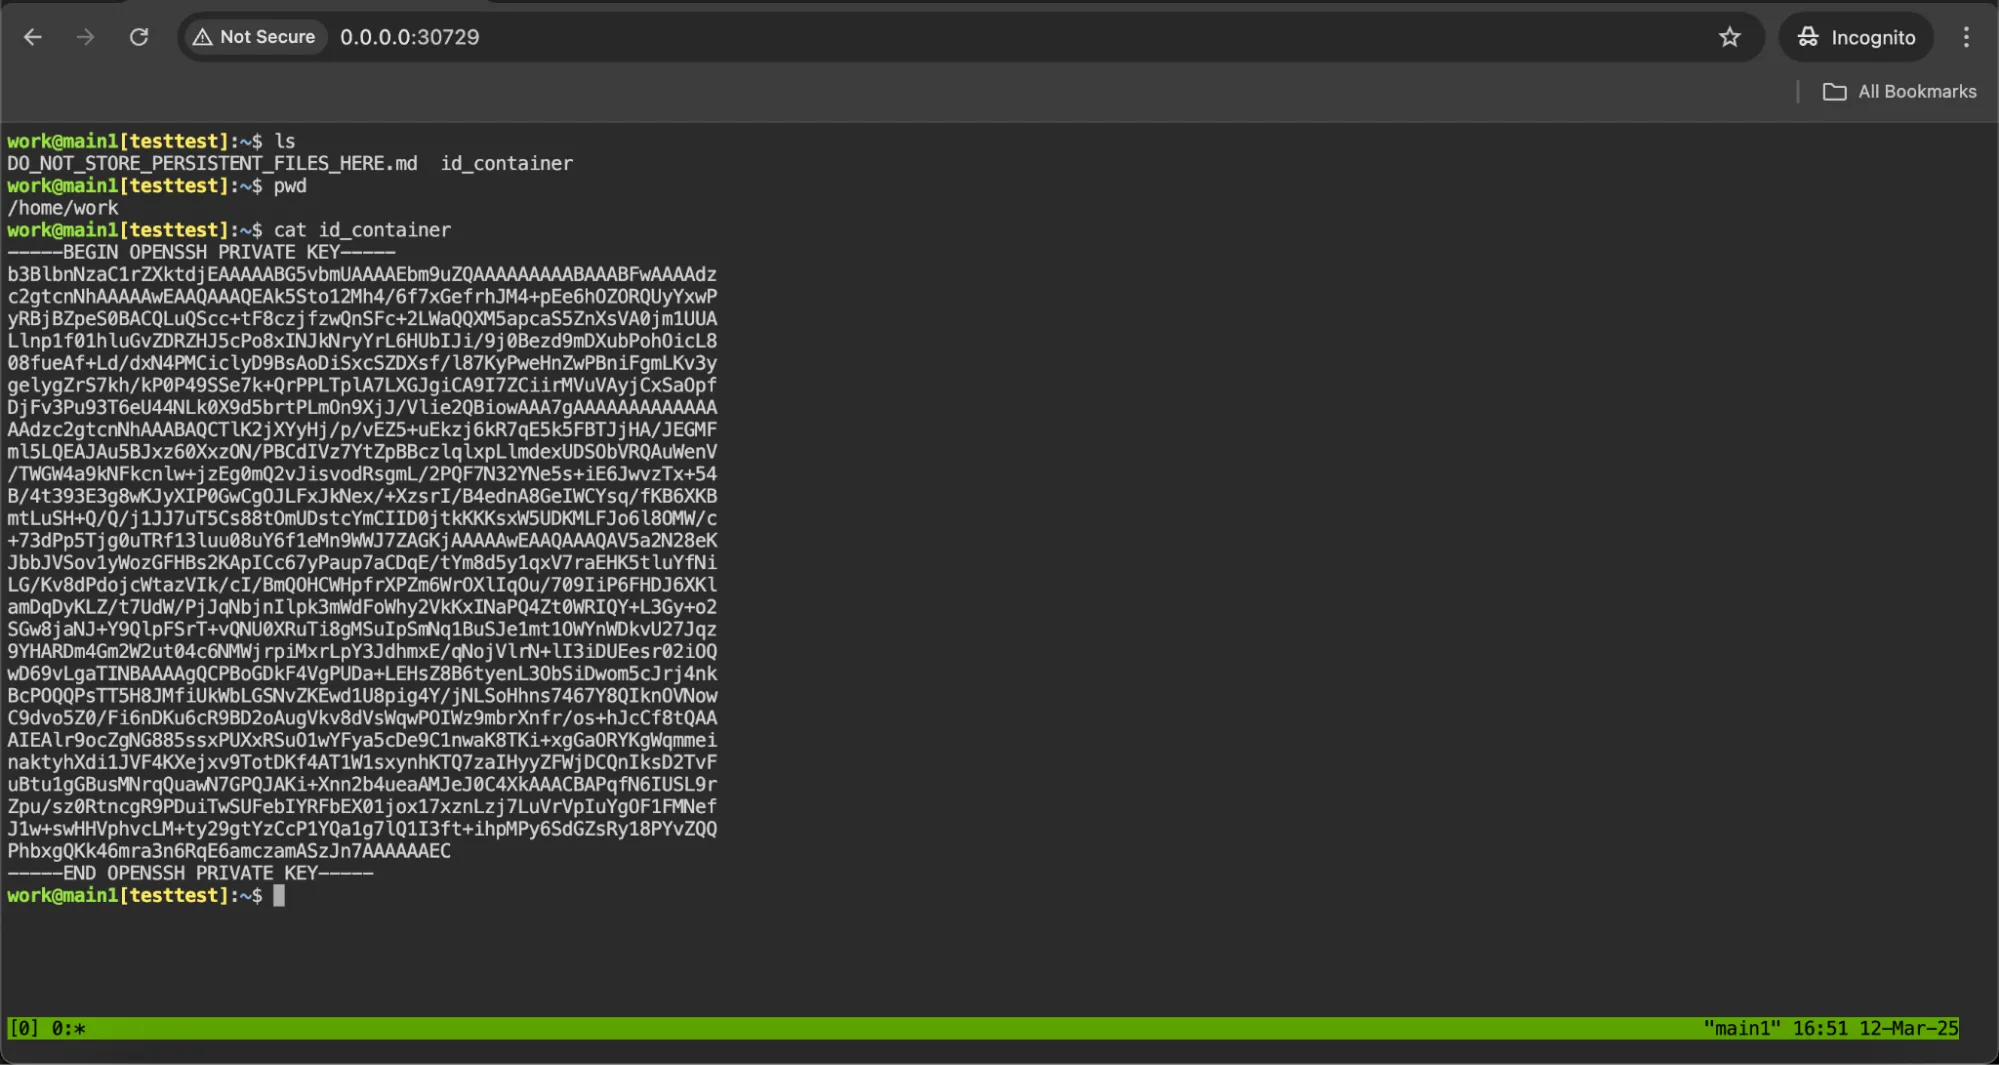
However, while simulating the threat actor, we access the same URL in an “incognito window” — eliminating any cache, cookies, or login credentials — we can still reach it, demonstrating the absence of proper authorization controls.
Related SAI Security Advisory
September 8, 2026
MLflow Vulnerability Report
A malicious MLflow model artifact can cause code execution during mlflow.pyfunc.load_model. The loader reads import settings from the model’s MLmodel file and imports the specified module without an allowlist or trust check, allowing attacker-controlled code in the artifact to run on the loading machine.
August 27, 2026
Netron Vulnerability Report
Reflected XSS in Netron versions <=9.1.2 on desktop application through unsanitized node names allows an attacker to hide certain nodes, perform port scanning or abuse a Chrome n-day to achieve Remote Code Execution.